



When Digital Risk Meets Physical Consequence
The New Reality of Industrial Operations
Industrial organizations across Pakistan — fertilizer, oil & gas, and power generation — are undergoing rapid digital transformation. Plants that once relied on isolated control systems now depend on remote monitoring, predictive maintenance, centralized dashboards, and vendor connectivity. These advancements deliver efficiency and reliability, but they also introduce a new category of risk: cyber threats capable of disrupting physical operations.
Industrial cybersecurity is no longer an IT responsibility alone. It is now a core operational risk affecting safety, production continuity, regulatory compliance, and corporate reputation.
A modern plant trip is no longer caused only by mechanical failure or process upset. Increasingly, it can originate from a compromised laptop, unauthorized remote session, or a misconfigured network connection.
Why Industrial Risk Is Different from Corporate Cyber Risk
Traditional cybersecurity programs evolved to protect information — emails, financial records, and intellectual property. Industrial environments protect something fundamentally different: the physical process.
In corporate IT, systems can be patched, rebooted, or isolated with limited consequence. In operational environments, a controller reboot can stop a compressor, a blocked communication path can trip a boiler, and an unauthorized command can damage rotating equipment.
The priority hierarchy changes completely:
- Safety
- Availability
- Integrity
- Confidentiality
For industrial organizations, cybersecurity is therefore closer to process safety than to data protection. It must be engineered into operations rather than managed as a software deployment.
Why Plants in Developing Economies Face Higher Exposure
Facilities in regions like South Asia and the Middle East often operate complex plants with long equipment lifecycles. Many control systems remain in service for 15–25 years — far longer than traditional IT systems.
These systems were designed for reliability and determinism, not security. As a result, they frequently lack authentication, encryption, and monitoring capabilities. When digital initiatives introduce connectivity — historians, remote support, cloud analytics — the protective isolation unintentionally disappears.
Common exposure pathways observed in regional industry include:
- Vendor remote access left permanently enabled
- Shared engineering passwords
- Flat plant networks without segmentation
- Engineering laptops moving between units
- USB-based software transfers
- Direct integration of control systems with corporate networks
Most successful industrial cyber incidents do not rely on sophisticated attackers. They exploit operational convenience.
Consequences: From Cyber Event to Production Loss
Unlike corporate breaches, industrial cyber incidents produce immediate operational impact. Consequences may include:
- Plant shutdowns lasting days
- Damage to compressors, turbines, or drives
- Safety system impairment
- Off-spec product and quality losses
- Environmental releases
- Supply disruption across downstream industries
For a fertilizer or energy complex, a multi-day outage can affect national supply chains, not just company revenue. This elevates cybersecurity from a technical issue to a strategic business risk.
A Practical Framework for Industrial Protection
Global standards such as ISA/IEC 62443 emphasize risk-based protection rather than product deployment. The most important principle is segmentation — separating business networks from operational networks and controlling communication between them.
Effective programs focus on discipline rather than complexity:
- Maintain a complete inventory of control assets
- Separate IT and OT networks with controlled gateways
- Enforce role-based access instead of shared credentials
- Monitor and log remote connections
- Test controller backups regularly
- Implement formal logic change approval procedures
- Review security alarms as part of routine operations
Organizations often discover that foundational controls reduce risk more effectively than advanced security tools.
The Human Factor: Operations as the First Line of Defense
In industrial incidents worldwide, the initial trigger is commonly human action — not malicious intent but routine behavior. Plugging in a vendor USB, bypassing controls during troubleshooting, or temporarily opening remote access can unintentionally expose the plant.
Therefore cybersecurity awareness must extend beyond IT teams. Operators, engineers, maintenance technicians, and contractors all form part of the security boundary. When operations teams recognize cyber anomalies the same way they recognize abnormal process conditions, detection improves dramatically.
Cybersecurity maturity begins when personnel treat unexpected system behavior as a process alarm, not just a computer issue.
Preparedness: Responding Without Creating a Safety Event
No industrial facility can guarantee prevention. The differentiator is response readiness.
An effective response plan defines:
- Who isolates the network
- Who validates process safety conditions
- How operations continue in manual mode
- How systems are restored and verified before restart
Restarting after a cyber event is closer to post-maintenance commissioning than IT recovery. Safety validation must precede production recovery.
Executive Perspective: Cybersecurity as Operational Reliability
Industrial cybersecurity should be governed similarly to mechanical integrity and safety management systems. Leadership involvement is critical because the risk tradeoffs are operational, not technical.
Key executive actions include:
- Assign joint ownership between operations and IT
- Integrate cyber risk into enterprise risk management
- Evaluate digital initiatives with security impact assessments
- Fund lifecycle maintenance, not one-time projects
Organizations that treat cybersecurity as compliance spend continuously without reducing risk. Organizations that treat it as reliability improve uptime and resilience.
Artificial Intelligence: Threat Multiplier and Defense Enabler
The next phase of industrial cybersecurity will be shaped by artificial intelligence. AI lowers the barrier for attackers by automating reconnaissance, generating convincing phishing messages, identifying weak configurations, and even crafting malware capable of adapting to industrial environments. Instead of targeting specific companies, attackers will increasingly deploy scalable automated campaigns searching for the easiest operational entry point. This makes every connected plant a potential target regardless of size or geography.
At the same time, AI provides powerful defensive capability. Advanced monitoring systems can now learn normal process behavior and detect subtle anomalies long before traditional alarms activate — such as unexpected controller communications, unusual command sequences, or deviations between process physics and digital signals. In complex facilities where thousands of signals exist, human operators alone cannot identify early indicators of compromise, but AI-assisted monitoring can.
The strategic implication for leadership is clear: AI will not simply be another tool but a force multiplier on both sides. Organizations that integrate AI into operational monitoring, maintenance analytics, and security detection will improve resilience. Those that delay adoption will face attackers operating at machine speed while defending manually.
Industrial cybersecurity programs must therefore evolve from periodic assessment to continuous intelligence-driven monitoring.
Conclusion
The convergence of automation and connectivity has permanently changed industrial risk profiles. Cybersecurity is no longer about protecting computers — it is about protecting production, safety, and national infrastructure continuity.
In modern industry, reliability depends equally on mechanical integrity and digital integrity. The most resilient organizations will be those that embed cybersecurity into engineering culture, operational discipline, and leadership decision-making.
Industrial cybersecurity is ultimately not a technology upgrade. It is an operational philosophy.
Author Bio
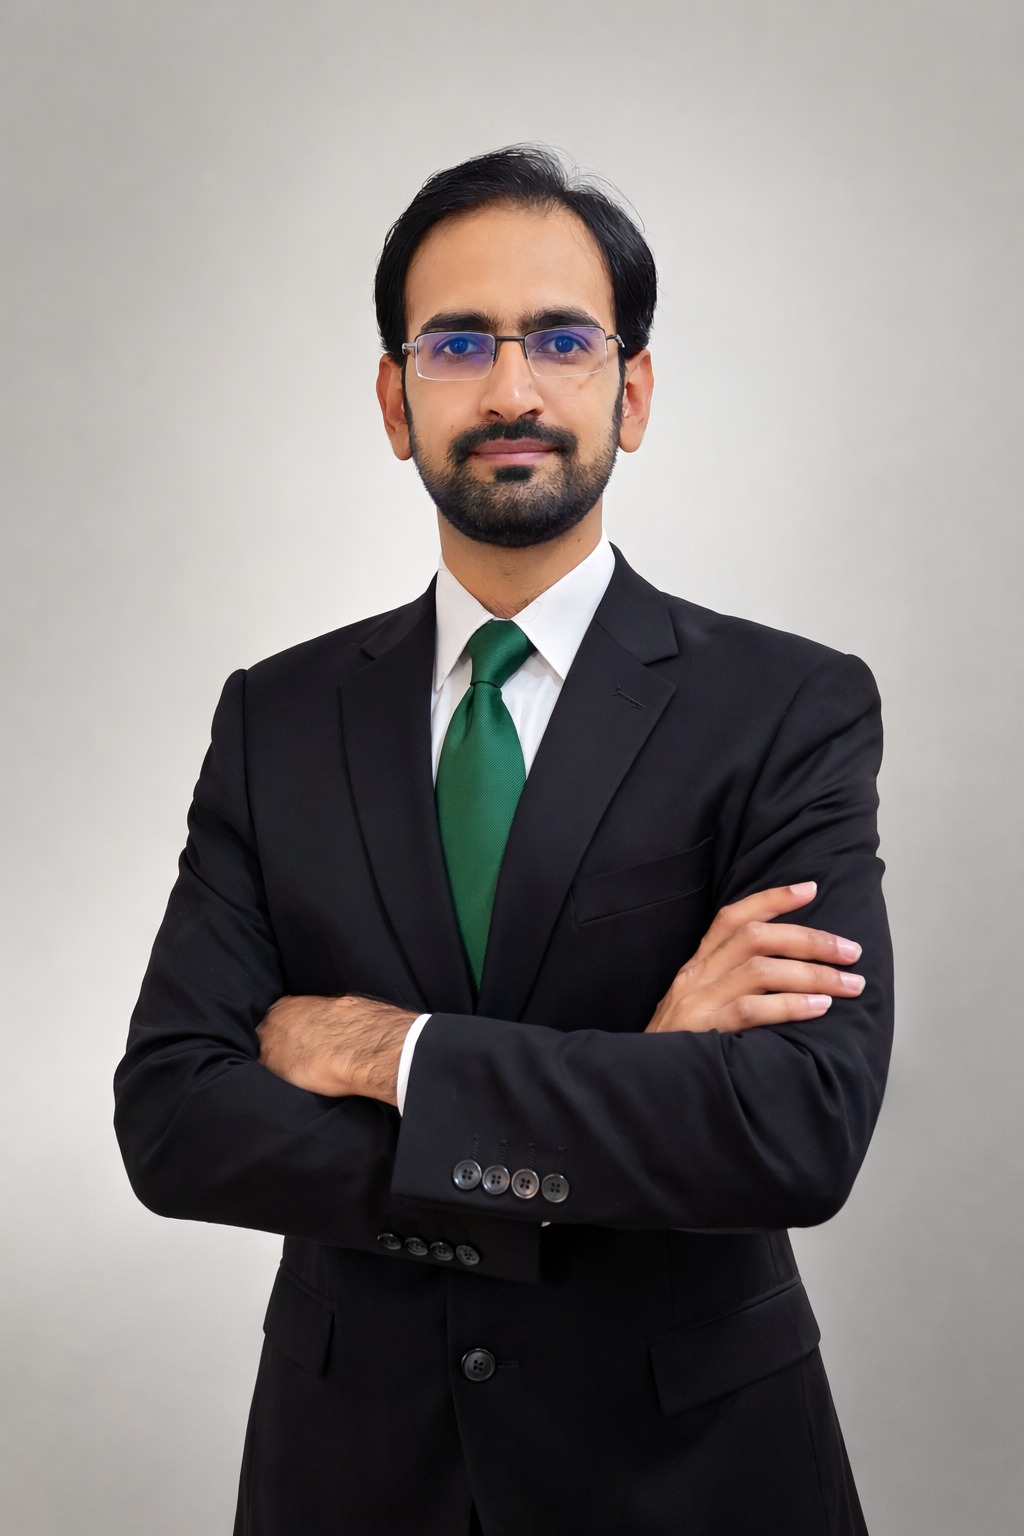 Asad Naeem is an Instrument, Control Systems & OT cybersecurity professional with over a decade of experience in the fertilizer and oil & gas sectors. He specializes in industrial automation, safety instrumented systems, and operational technology cybersecurity. His work focuses on integrating reliability, safety, and cybersecurity practices within complex process industries and advancing secure digital transformation in industrial environments.
